Installation
endpoint, key, registry.
From the unzipped folder to a console that reads the chain through your own endpoint. Plan about 20 minutes.
01Build
- Install packages
flutter pub get - Check it
flutter analyze # expect: No issues found flutter test # expect: All tests passed - Run the console with your operator passcode
flutter run -d macos --dart-define=SLUICE_OPERATOR_PASSCODE=choose-your-own    # desktop
flutter run -d chrome --dart-define=SLUICE_OPERATOR_PASSCODE=choose-your-own   # or in the browser
On Windows run these from PowerShell, WSL or Git Bash; the tool/*.sh scripts need WSL or Git Bash.
Both macos/Runner/*.entitlements files include com.apple.security.network.client, so the sandboxed desktop app can reach your RPC endpoint.
02The operator passcode
The console is where the projects, the funding wallets, the operator fee and its fee wallet, and the endpoints are set. So it is not open to whoever starts the app: it is compiled into a build only when you give that build a passcode, and it opens only after the passcode is entered.
- Choose a passcodeSix characters or more. Shorter values are ignored, so a placeholder like
1234cannot publish a console. - Pass it at build time
flutter build macos --release --dart-define=SLUICE_OPERATOR_PASSCODE=choose-your-own flutter build web --release --dart-define=SLUICE_OPERATOR_PASSCODE=choose-your-own - UnlockThe app opens on OPERATOR CONSOLE. Type the passcode and press Unlock. The unlock lasts until the app is closed or the page is reloaded; it is never written to disk. After every third wrong attempt entry pauses for 3, then 6, then 12 seconds.
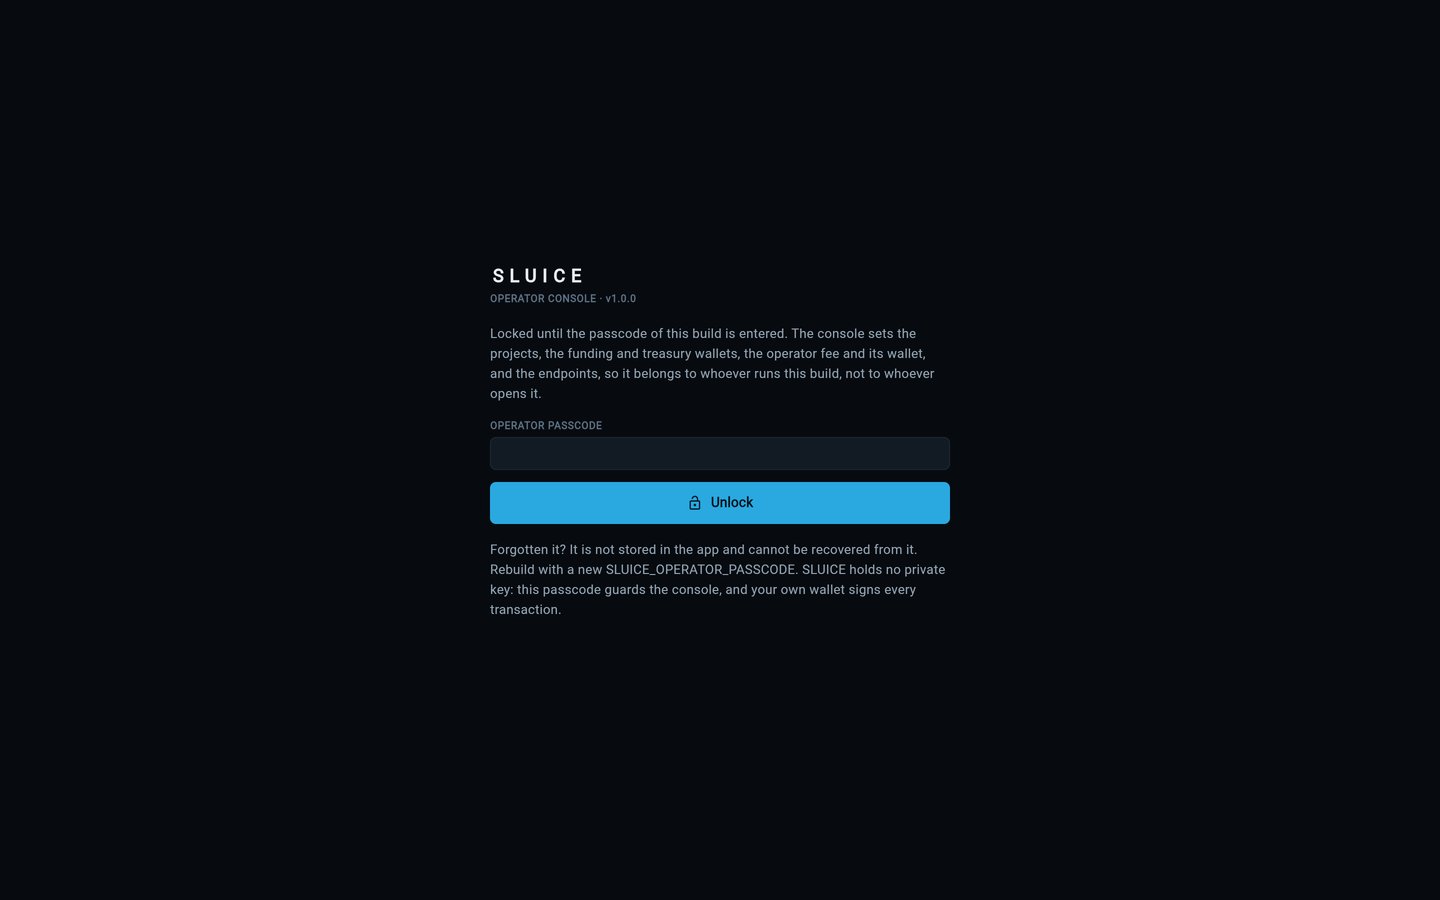
It opens on NO OPERATOR CONSOLE IN THIS BUILD with the command to add one. Nobody can create a project or change a wallet, a fee or an endpoint with it.
It keeps other people out of the console of a build you host or hand on. It is not a wallet password: SLUICE holds no private key and signs nothing, so there are no funds behind it. Forgotten it? It cannot be read back from the app; rebuild with a new one. Your projects and rounds on that device are kept.
03Your RPC endpoint
Required before a real round
- Get an endpointFrom any Solana RPC provider, on your own account.
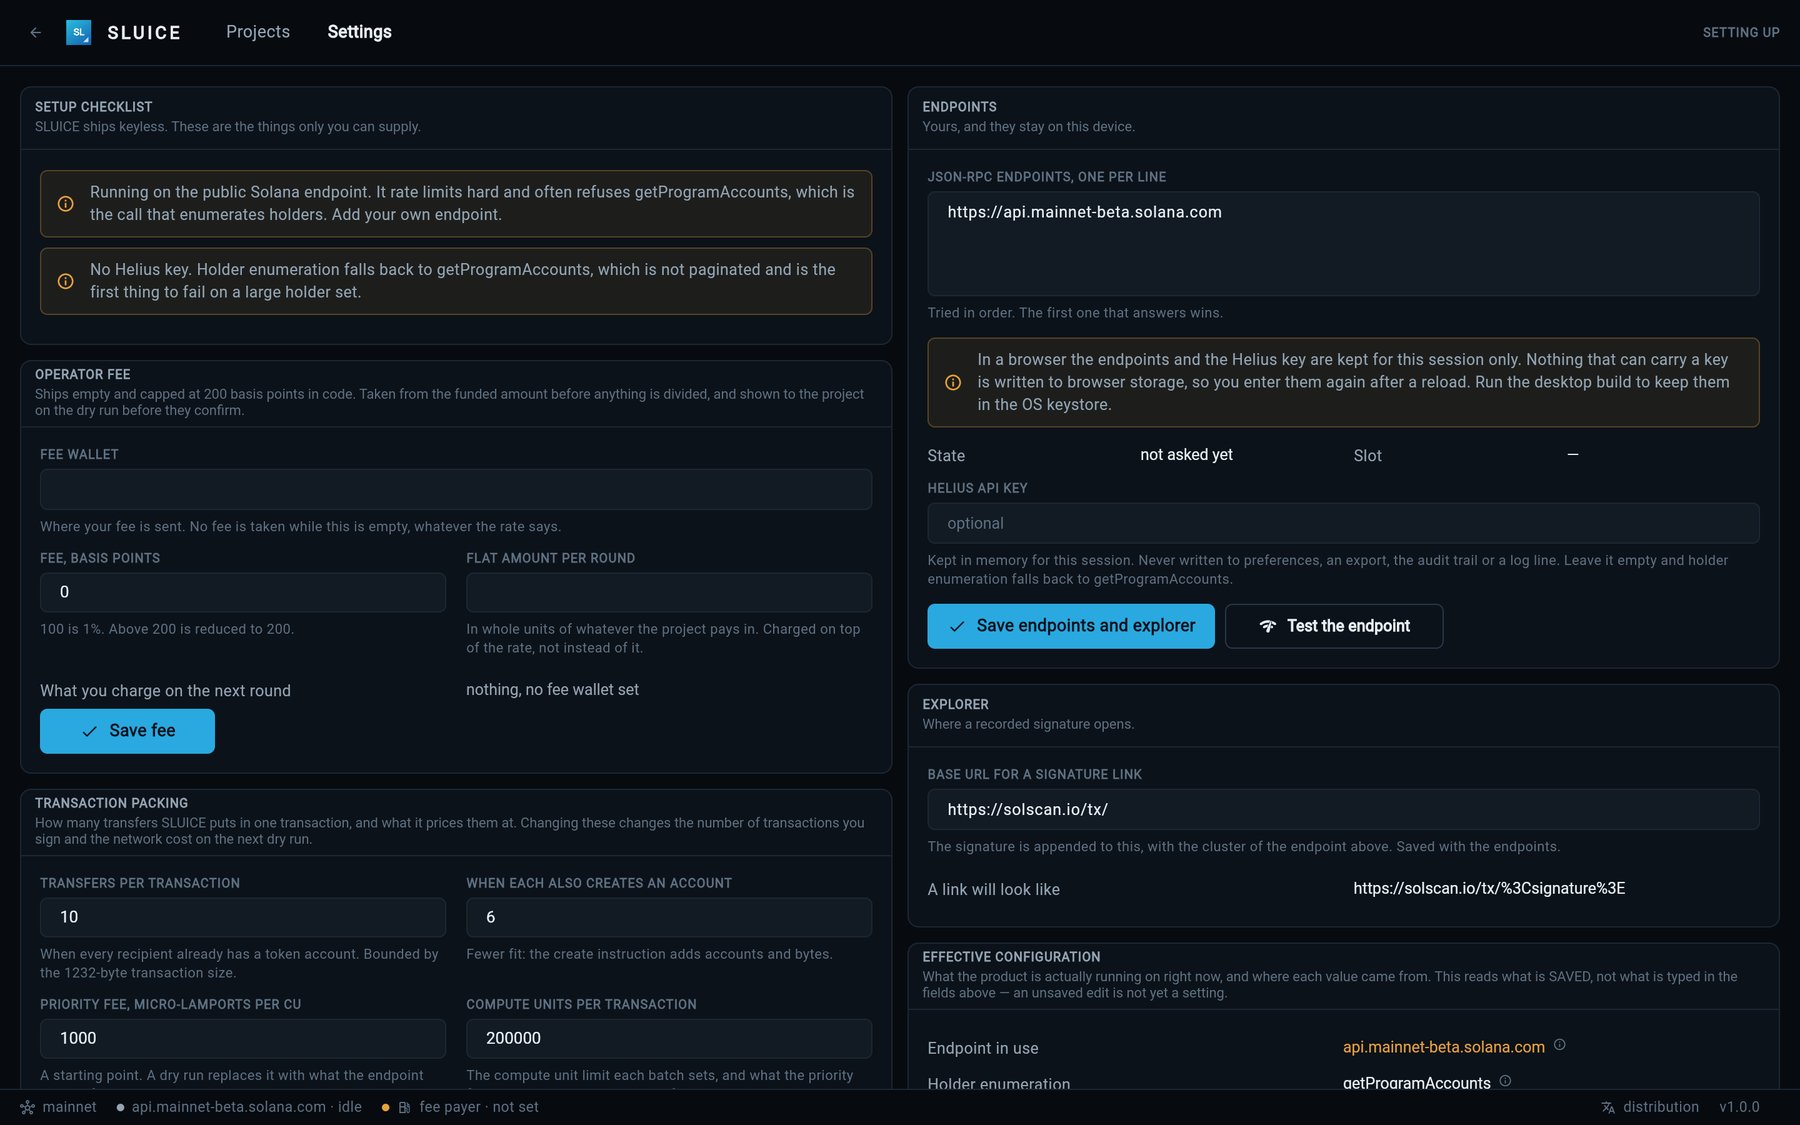
- Open Settings → EndpointsOn first run, Endpoints and keys takes you there.
- Paste your URLsIn JSON-RPC endpoints, one per line. They are tried in order and rotated on failure.
- Save and testSave endpoints and explorer, then Test the endpoint. The state and current slot appear.
On macOS, iOS and Android the endpoint list is saved in the app's local preferences with the other operator settings (lib/core/config/local_store.dart); the Helius key goes to the OS keystore. In a browser neither is written anywhere: a private endpoint URL often carries a key, and browser storage is readable by any script on the page, so the web build keeps the endpoints and the key for the session only. You enter them again after a reload. If your provider puts a key inside the URL, restrict that key to your domain in the provider's dashboard.
04Your Helius key
Recommended Settings → Endpoints → Helius API key. The key is written to the OS keystore (Keychain on macOS and iOS, Keystore on Android) under sluice.vault.helius_api_key. It is never written to preferences, an export, the audit trail or a log line; the rest of the app only sees whether one is present. Remove the stored key deletes it. In the web build the key is held in memory for the session only.
Helius does not allow sharing a key, so SLUICE ships none.
05Verify the program registry
Exclusions → Verify the registry on chain. SLUICE ships a list of AMM, bonding-curve and order-book programs, each marked unverified. This calls getAccountInfo on each ID and marks those that exist and are executable. An ID that does not verify is struck through and no longer used as a label.
Detection does not depend on it: a pool vault is caught first because its authority is off the ed25519 curve, which needs no list.
06Where your data lives
On the machine SLUICE runs on. Settings, projects and the audit trail are in the app's local preferences; credentials are in the OS keystore. In a browser the endpoints and the Helius key are kept in memory for the session only; projects and the audit trail are in browser storage. Nothing is uploaded. Back up each round by exporting its Audit bundle · JSON: it carries the snapshot, the exclusions and the plan, so a round can be checked and reproduced from it.
07Checklist
- The console opens only with your passcode.
- Test the endpoint answers with a slot.
- The setup checklist in Settings has no warning left, or you know why.
- The registry is verified.